

Rank Math PRO Backdoor: How to Check and Clean Your Site


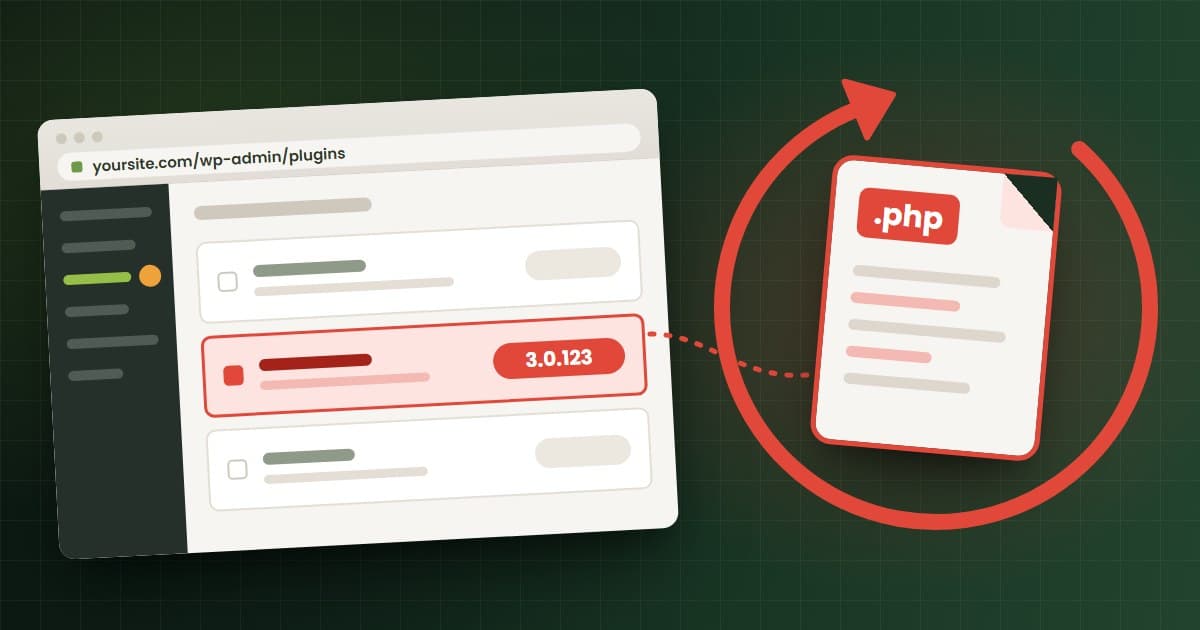
The Rank Math PRO backdoor reached WordPress sites through copies of Rank Math SEO PRO 3.0.123 downloaded or updated between 20:02 UTC on October 15, 2026 and 07:12 UTC on October 16, 2026.1 If your site installed and activated a copy from that window, Rank Math says to treat the site as compromised. The free Rank Math plugin on WordPress.org is not affected, and 3.0.124 is the clean release.1
Updating does not clean an infected site. Wordfence says installing 3.0.124 "does not remove files, accounts, or scheduled tasks that the malware may already have created elsewhere."2 Rank Math says the backdoor can rebuild itself when someone visits the site.1 This guide covers how to tell whether you were hit and the cleanup order that stops the rebuild.
The short version
- What: Some Rank Math SEO PRO 3.0.123 packages carried a backdoor. The CVE record, issued by Wordfence, calls it a "supply-chain compromise."3
- When: An 11-hour, 10-minute window, from 20:02 UTC on October 15 to 07:12 UTC on October 16, 2026.1
- Who: PRO sites that installed and activated a 3.0.123 copy from the October 15 to 16 window. Running 3.0.123 does not by itself prove a site is compromised.3
- Severity: CVE-2026-111862, rated 9.8 out of 10 (Critical).3
- What it does: It keeps access, communicates with rank1cdn[.]com, rebuilds hidden backdoors on page visits, and can expose any password or key the web server can read.3
- Fix: Snapshot the site, then restore a backup from before 20:02 UTC on October 15, or clean in a set order. Then rotate every credential and install 3.0.124 from your Rank Math account.1
What happened to Rank Math PRO 3.0.123?
Rank Math released PRO 3.0.123 on October 7, 2026, with two bug fixes.7 On October 16, the company published a notice saying it had "recently identified a security issue affecting a limited number of users" who downloaded 3.0.123 between 20:02 UTC on October 15 and 07:12 UTC on October 16. The notice says the affected plugin files "contained malware that could compromise your website." Rank Math removed those files and released 3.0.124.1
A site showing 3.0.123 might hold a clean copy or a tampered one. The bad copies came from a window that opened eight days after 3.0.123 first shipped, and a copy fetched before 20:02 UTC on October 15 falls outside the incident.14 The CVE record also says "version 3.0.123 alone is not sufficient to establish compromise."3
Patchstack describes the incident as "a supply chain attack against the Rank Math SEO PRO infrastructure." For that reason, it says, a virtual-patching firewall rule cannot mitigate it.4
Who is affected by the Rank Math PRO backdoor?
The backdoor affects only Rank Math SEO PRO customers. Rank Math says sites on the free WordPress.org plugin are "not affected, and no action is needed."1 The free plugin is at version 1.0.280, last updated October 6, 2026, and WordPress.org lists it at 4+ million active installs.10 That figure belongs to the free plugin. Rank Math has not said how many customers received a tampered copy.14
Rank Math sorts PRO customers who got 3.0.123 between 20:02 UTC on October 15 and 07:12 UTC on October 16 (the window) into three cases:1
| Your situation | What Rank Math says to do |
|---|---|
| Installed and activated 3.0.123 from the window | Treat the site as compromised and follow the recovery steps |
| Installed 3.0.123 from the window but never activated it | Delete the plugin files, install 3.0.124 from your account, and run a security scan |
| Downloaded the zip but never installed or activated it | There is "no indication from this incident alone" that the site was compromised |
The first case still applies if you have since updated to 3.0.124, because the update does not remove what the malware created.2
Rank Math has emailed some customers.1 Wordfence reports that "Rank Math says it has records identifying users who downloaded an affected copy," a claim that does not appear in Rank Math's own notice.2
When did the Rank Math PRO 3.0.123 compromise happen?
All times are UTC.
| Date (2026) | What happened |
|---|---|
| October 7 | Rank Math releases PRO 3.0.123 with two bug fixes.7 |
| October 14, 19:31 | The domain rank1cdn[.]com is registered through NiceNIC, with Cloudflare nameservers.8 |
| October 15 | The CVE record gives this as the discovery date.3 |
| October 15, 20:02 | Tampered 3.0.123 downloads and updates begin.1 |
| October 16, 07:12 | The window closes, 11 hours and 10 minutes later.1 |
| October 16 | PRO 3.0.124 appears in the changelog with the same two bug-fix lines and no security note.7 |
| October 16, 20:32 | Rank Math publishes its security notice.1 |
| October 17, 03:41 | Wordfence publishes its advisory, which is the evening of October 16 in US time zones.2 |
| October 17 | Patchstack and WPScan add the backdoor to their databases.45 |
| October 19, 16:35 | CVE-2026-111862 is published. The NVD lists it as "Deferred," with no score of its own.36 |
The domain was registered about 24 and a half hours before the window opened.18
What does the Rank Math PRO backdoor do?
The CVE record says the malware may keep persistent access, contact rank1cdn[.]com, rebuild hidden backdoors when pages are visited, and expose WordPress logins, database credentials, API keys and any other secret the web server can read.3 Three of its behaviors decide how you clean up:
- It rebuilds itself. Rank Math says the malware "can recreate its hidden backdoor whenever someone visits the website." Remove files before you disable that mechanism and the cleanup "may not resolve the issue."1
- It reaches past the plugin. The attacker may leave files, admin accounts, scheduled tasks and changes "outside your WordPress installation."1
- Updating and deactivating miss it. Version 3.0.124 replaces the plugin but leaves the malware's other changes in place.2 Rank Math adds that "Deactivating the plugin alone is not sufficient."1
BleepingComputer found a PHP file on VirusTotal, named cache-preloader-fff033 (1).php, that shares several of Rank Math's indicators: the xmmqhn key, the _np5pvf754c option, the #ms6v46 cron tag and the wpsupport_ admin prefix.15 BleepingComputer reports the file can run commands, change the database, and steal AWS, Cloudflare, Google Cloud and Azure credentials and SSH keys. BleepingComputer could not confirm the file came through the plugin.15 If cloud keys sit anywhere the web server can read, rotate them regardless.
How do I check if my site is affected by Rank Math PRO 3.0.123?
Checks you can run without a developer
- Confirm you run PRO. Go to Plugins > Installed Plugins and look for Rank Math SEO PRO. If you only have the free Rank Math SEO plugin, this incident does not affect you.1
- Work out whether the site took 3.0.123 in the window. The window ran from 4:02 p.m. EDT on October 15 to 3:12 a.m. EDT on October 16. In the UK, that is 9:02 p.m. to 8:12 a.m. BST.1 Check your inbox for an email from Rank Math, and check any activity log or host update log for a Rank Math PRO update in those hours. Do this even if the site now shows 3.0.124.
- Look for rogue administrators. Go to Users > All Users and filter by Administrator. Rank Math flags usernames that start with
wpsupport_followed by random characters, and email addresses ending in@wp-mail[.]net.1 - Review Application Passwords. In each administrator's profile, revoke any Application Password you don't recognize. Rank Math's list does not include this check. We add it because Application Passwords grant access to the WordPress REST API.16
- Find your last backup from before 20:02 UTC on October 15. Rank Math's recommended fix depends on having one.1
Indicators of compromise for your host or developer
Every indicator below comes from Rank Math's notice.1
| Type | Indicator | Where to look |
|---|---|---|
| Domain | rank1cdn[.]com | Outbound connections, firewall and DNS logs |
| Database rows | _uf6qdn2hmm, t8krdk990phb, _np5pvf754c |
The option_name column of wp_options |
| Fake core file | wp-includes/class-wp-cache-util.php |
wp-includes/ (not a real core file) |
| Hidden PHP | Suspicious PHP files | wp-content/mu-plugins/, other plugins' folders, the inc/, includes/ and lib/ folders of non-default themes, Rank Math's own includes/ folder, and uploads/ |
| Code patterns | base64_decode with XOR loops, the key xmmqhn, proc_open, PHP-FPM socket code |
Any PHP file |
| Admin accounts | Usernames starting wpsupport_, emails ending @wp-mail[.]net |
Users screen, or wp user list --role=administrator |
| PHP execution | .htaccess rules that let .cache files run as PHP, and .cache files containing PHP |
The root .htaccess and any subfolder |
| Scheduled tasks | Entries tagged #ms6v46 |
The web server user's system crontab, plus wp cron event list |
| Server | SSH authorized_keys, other users' crontabs, running processes |
Any location outside the site where the web server user can write |
Rank Math has not published file hashes or IP addresses.114 If you find none of these signs, Wordfence warns that their absence "does not, by itself, prove that a website is clean."2
How do I clean up the Rank Math PRO backdoor?
Rank Math's first choice is a restore. Put back the site and database from a backup made before 20:02 UTC on October 15, scan it with a tool such as Wordfence or Sucuri, rotate every credential, then install 3.0.124.1 Take the snapshot in step 1 below before you restore, because the restore overwrites the evidence. A restore also only replaces the site and its database. Rank Math warns the attacker may have made changes outside the WordPress installation, so still run the server checks in the indicator table, or ask your host to.1 Our WordPress backup strategy guide covers keeping copies off the server so that option exists.
Without a clean backup, work in this order. Steps 3 through 8 follow Rank Math's notice. Steps 1 and 2 are our additions.
1. Snapshot the infected site
Copy all files and the database before you change anything, and store the copy off the server. WordPress.org recommends this snapshot even when the site is infected.13 The copy preserves evidence and gives you a fallback. Never restore from it.
2. Take the site offline
Rank Math says the backdoor rebuilds when someone visits.1 Ask your host for a server-level holding page or an access block while you work, so visits stop reaching WordPress. A maintenance-mode plugin still loads WordPress on every request, so it is the weaker option. Our hacked WordPress site playbook walks through this first hour in more detail.
3. Stop the rebuild before you delete anything else
Rank Math says to finish all three of these before moving on:1
- Delete the entire
rank-math-profolder through your host's file manager or SFTP. - Delete the three
wp_optionsrows named_uf6qdn2hmm,t8krdk990phband_np5pvf754c, using a tool such as phpMyAdmin. - Block outbound connections to rank1cdn[.]com at your host or firewall, if they support it.
4. Remove what the attacker left
Work through every indicator of compromise in Rank Math's list: hidden PHP files, the fake class-wp-cache-util.php, the .htaccess and .cache changes, PHP files in uploads/, and the server-level checks.1 On shared hosting you can't reach system crontabs or SSH keys yourself, so Rank Math says to ask your host to check them.1
5. Reinstall clean copies from verified sources
- WordPress core. Run
wp core verify-checksums, then reinstall core from an official source.1 - Other plugins and themes. Reinstall from their official sources.1 Upload fresh copies over SFTP instead of using the reinstall options in wp-admin. WordPress.org warns that those installers "often only overwrite existing files, and hacks often introduce new files."13
- Rank Math PRO. Type rankmath.com into your browser, log in, and download 3.0.124 from your account. Rank Math says it "will never send login or download links by email," so treat any email carrying one as phishing.1 Install the zip under Plugins > Add New > Upload Plugin.12
You cannot verify PRO files against WordPress.org. When we checked on October 20, its checksum service had no file for PRO 3.0.123 under either seo-by-rank-math-pro or rank-math-pro, though it had one for the free plugin.9 So wp plugin verify-checksums --all will not cover PRO, and Rank Math has published no hashes.14 Wordfence's advice is to "compare those files with a clean copy downloaded directly from the developer."2
6. Rotate every credential
Rank Math says to rotate credentials even after a restore, and to assume any secret the site could read was exposed.1 Its list covers:1
- WordPress account passwords
- The database username and password in
wp-config.php - WordPress security keys and salts
- Payment gateway keys, SMTP credentials and other API keys
- Hosting panel, FTP/SFTP and SSH credentials, plus secrets in environment variables
- Two-factor authentication for administrators
New keys and salts log everyone out.13 They can also break Rank Math's account connection. Rank Math encrypts its stored account data with LOGGED_IN_KEY and LOGGED_IN_SALT, so after a reset PRO may show "Automatic update is unavailable for this plugin." The fix is to add RANK_MATH_ENCRYPTION_KEY and RANK_MATH_ENCRYPTION_SALT to wp-config.php, then disconnect and reconnect your account under Rank Math SEO > Dashboard > Help.11
WordPress.org also says to change your passwords a second time once the site is confirmed clean.13
7. Check admins and scheduled tasks again
Run wp user list --role=administrator and wp cron event list, and recheck the system crontab for #ms6v46.1 Review Application Passwords for every administrator and revoke any you don't recognize, in the dashboard or with the wp user application-password commands.16
8. Monitor in the days after
Scan the site, verify checksums, watch outbound connections, and check whether any file you removed comes back.1 A returning file means the cleanup missed something, so go back to step 4 and bring in your host or a security professional.1 Once the site is clean, update WordPress core too. On the 7.1 branch that means at least 7.1.3, covered in our WordPress 7.1.3 guide.
What has Rank Math said about the security incident?
- It says it "recently identified" the issue but has not named who found it. The CVE record credits no researcher.13
- It removed the affected files and released 3.0.124.1 The 3.0.124 changelog repeats the two 3.0.123 bug-fix lines and says nothing about security.7
- Some customers "may need to reset their account password." The notice gives no reason.1
- It is "taking steps to reduce the risk of similar incidents in the future," without saying what those steps are. Support tickets go through rankmath.com/support.1
BleepingComputer asked Rank Math how many sites were affected and how the attack started. It had received no reply when it published on October 19.15
What is still unknown about the Rank Math PRO backdoor?
- How the files got in. Rank Math has not described the cause.1
- How many sites received it. Rank Math says "a limited number of users" and gives no count.1
- Whether automatic updates delivered it. Rank Math's notice covers anyone who "downloaded or updated" in the window.1 The Hacker News reports that Rank Math has not said whether automatic updates carried the malware.14
- Hashes and a code analysis. Rank Math has published no hashes, and neither its notice nor Wordfence's advisory analyzes the code. What is confirmed about the malware's behavior comes from Rank Math's notice.14
- Who did it. Nobody has been named.14
- Whether the VirusTotal sample is part of it. BleepingComputer could not confirm the link.15
The Hacker News lists other 2026 supply-chain incidents at WordPress vendors, including Smart Slider 3 Pro in April and ShapedPlugin in June, and says nothing published links them to this one.14 Our post on whether to auto-update WordPress plugins covers pairing updates with monitoring for this kind of risk.
What should Rank Math PRO users do now?
Today
- List every site running Rank Math SEO PRO and find out which took 3.0.123 between 20:02 UTC on October 15 and 07:12 UTC on October 16.
- Check administrators for
wpsupport_usernames and@wp-mail[.]netemails. - On any affected site, snapshot it, take it offline, and stop the rebuild.
This week
- Restore from a backup made before 20:02 UTC on October 15, or finish the manual cleanup.
- Rotate every credential, add the Rank Math encryption constants, and install 3.0.124.
- Watch for files that reappear and for traffic to rank1cdn[.]com.
Frequently asked questions
Is the free Rank Math plugin affected by the backdoor?
No. Rank Math says the free version on WordPress.org is not affected and needs no action. Only PRO 3.0.123 copies from the October 15 to 16 window carried the malware.
Does updating to Rank Math PRO 3.0.124 remove the backdoor?
No. Version 3.0.124 replaces the plugin files, but Wordfence says it does not remove files, accounts or scheduled tasks the malware created elsewhere. An infected site needs a restore or a full cleanup.
My site runs Rank Math PRO 3.0.123. Is it infected?
Not necessarily. Rank Math limits the incident to copies obtained between 20:02 UTC on October 15 and 07:12 UTC on October 16. Check when your copy was installed, look for the indicators above, and contact Rank Math support if you can't tell.
Is deactivating Rank Math PRO enough to stop the malware?
No. Rank Math says deactivating the plugin alone "is not sufficient." Snapshot the site first, then delete the whole rank-math-pro folder, remove the three wp_options rows, and block rank1cdn[.]com before you clean anything else.
What is rank1cdn[.]com?
The CVE record says the malware communicates with it, and Rank Math tells site owners to block it. Registry records show it was registered on October 14, 2026, about a day before the tampered downloads began. Block outbound connections to it.
What is CVE-2026-111862?
CVE-2026-111862 is the identifier for the Rank Math PRO 3.0.123 backdoor. Wordfence issued it, and it was published on October 19, 2026. It is rated 9.8 out of 10 (Critical) and classed as CWE-506, Embedded Malicious Code.
If you want help
If you run Rank Math PRO on several sites and need to know which ones took a tampered copy, or you want a second set of eyes on a cleanup, send us the list through /start. You'll get a scoped estimate within 48 hours.
Sources
- Rank Math, "Rank Math PRO 3.0.123 Security Incident: How to Secure Your Website," published October 16, 2026, updated October 19, 2026 (page metadata). rankmath.com
- Wordfence, Alex Thomas, "PSA: Malware Found in Some Rank Math SEO PRO 3.0.123 Downloads," published 03:41 UTC October 17, 2026. wordfence.com
- CVE Program, CVE-2026-111862, "Rank Math SEO PRO 3.0.123 - Unauthenticated Embedded Malicious Code," published October 19, 2026. cve.org
- Patchstack Database, "WordPress Rank Math SEO PRO Plugin 3.0.123 is vulnerable to a high priority Backdoor," October 17, 2026. patchstack.com
- WPScan, "Rank Math SEO PRO 3.0.123, Backdoor via Supply Chain Compromise," added October 17, 2026. wpscan.com
- NIST National Vulnerability Database, CVE-2026-111862, checked October 20, 2026. nvd.nist.gov
- Rank Math, PRO changelog, versions 3.0.123 and 3.0.124, checked October 20, 2026. rankmath.com
- Verisign RDAP registration record for the domain rank1cdn[.]com (rdap.verisign.com, .com registry lookup), checked October 20, 2026. Not linked on purpose.
- WordPress.org plugin checksums service, checked by WitsCode on October 20, 2026. No file exists for Rank Math PRO 3.0.123 under seo-by-rank-math-pro or rank-math-pro; the free plugin's 1.0.280 file is present. downloads.wordpress.org
- WordPress.org Plugin Directory, Rank Math SEO (free plugin), checked October 20, 2026. wordpress.org
- Rank Math Knowledge Base, "How to Fix 'Automatic Update is Unavailable for this Plugin' Error in Rank Math," checked October 20, 2026. rankmath.com
- Rank Math Knowledge Base, "How to Upgrade to Rank Math PRO," checked October 20, 2026. rankmath.com
- WordPress.org Documentation, "FAQ My site was hacked," last updated July 26, 2026. wordpress.org
- The Hacker News, Swati Khandelwal, "Popular WordPress SEO Plugin Rank Math PRO Hijacked to Deliver Self-Restoring Backdoor," October 19, 2026. thehackernews.com
- BleepingComputer, Bill Toulas, "WordPress SEO plugin Rank Math compromised to backdoor websites," October 19, 2026. bleepingcomputer.com
- WordPress Developer Resources, Advanced Administration: Application Passwords, last updated October 14, 2026. developer.wordpress.org
Facts checked on October 20, 2026.
Comparing web agencies?
Send the brief. You get a scoped plan, a real timeline, and we tell you when another shop is the better fit.
- Rebuilds, redesigns, and migrations
- You own the code and the domain
- Scoped estimate within 48 hours
Working on something in WordPress?
Tell us what you are working on. You get a scoped estimate within 48 hours.
Keep reading
More from WordPress.
- WordPress
October 6, 2026
WordPress 7.1.3 Security Release: SQL Injection and XSS Fixes
WordPress 7.1.3 fixes seven core flaws, including SQL injection and stored XSS. See who is at risk, how to check your version and update, and what to do today.
- WordPress
October 1, 2026
CVE-2026-87902: Update to WordPress 7.1.2 and Check for a Breach
CVE-2026-87902 can let attackers run code on unpatched WordPress sites and is under attack. Check your version, update to WordPress 7.1.2 and look for a breach.
- Guides & Insights
October 19, 2026
SaaS Paid Ads Strategy: LinkedIn + Meta Playbook (2026)
A SaaS paid ads strategy for B2B pipeline: pick channels by ACV, structure LinkedIn and Meta, target accounts, test creative, and measure pipeline, not CPL.